CVE-2023-32268: cleartext LDAP credentials in MicroFocus Filr Appliance
A Filr administrator can retrieve, in cleartext, the LDAP service password used to synchronise Active Directory, opening a path to full domain controller compromise.
- CVE
- CVE-2023-32268
- Product
- MicroFocus (OpenText) Filr Appliance 3.0 build 4670
- CVSS
- 7.2
- Severity
- high
- Status
- patched
TL;DR
MicroFocus Filr Appliance 3.0 (build 4670) shows an administrator the service password used to synchronise users from Active Directory over LDAP. The password is masked in the interface, but it is returned in cleartext in the response of the RPC call that populates the configuration page. With that credential an attacker can authenticate to the domain controller and proceed with data exfiltration and lateral movement.
A vulnerability I found during a penetration test carried out in my work at Tinexta Cyber. Publication follows responsible disclosure: details are released only after the vendor’s patch.
Context
Filr is MicroFocus’s (now OpenText) product for file access and sharing from any device. In enterprise deployments it is integrated with Active Directory: a service account lets Filr synchronise domain users over LDAP.
The vulnerability surfaced during a penetration test on a client exposing Filr. Starting from administrative credentials of the product — i.e. an attacker or insider already holding privileged access to the application — it was possible to recover the password of the LDAP service account.
Details
| Vulnerability | CVSS v3.1 | Vector |
|---|---|---|
| LDAP Credential Disclosure | 7.2 (High) | AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H |
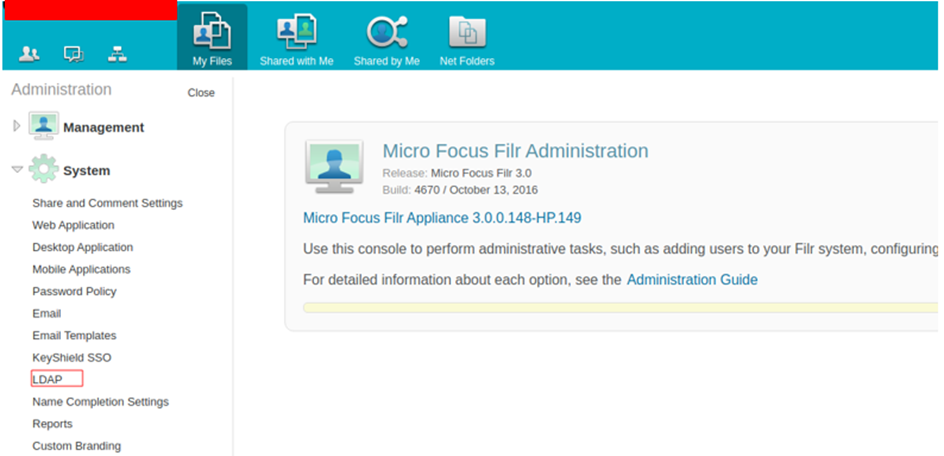
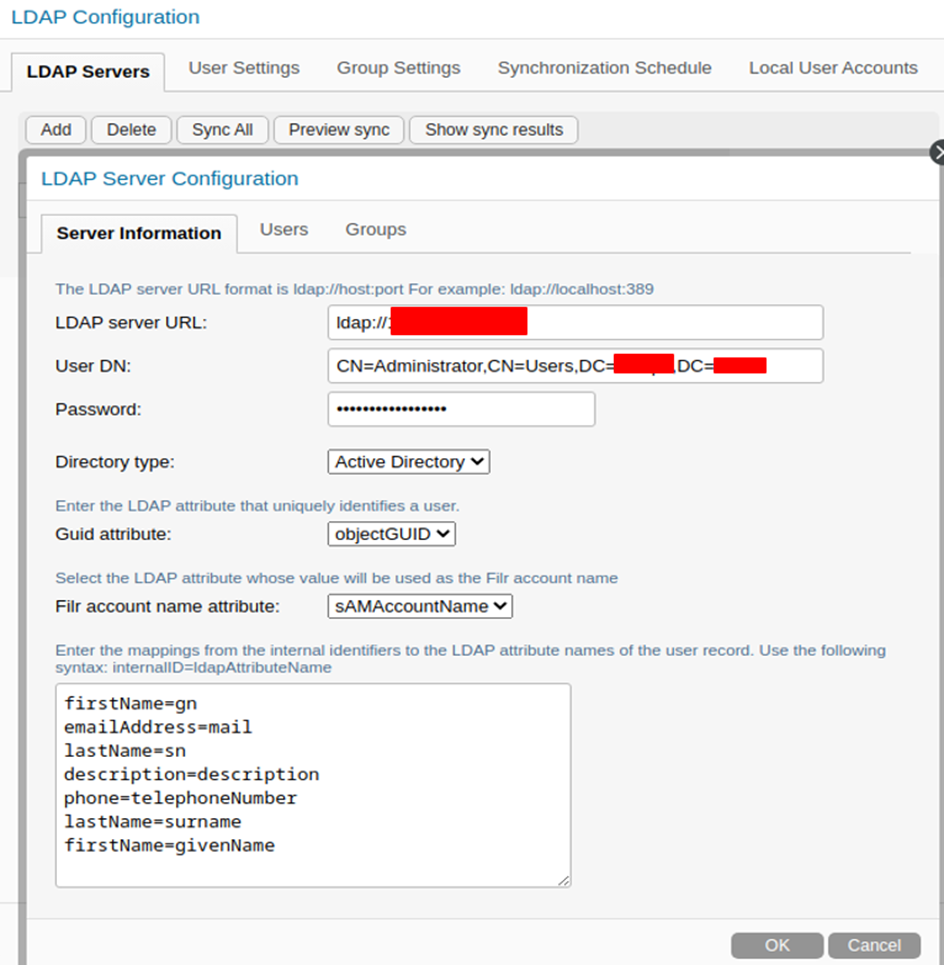
The web interface exposes, to a highly privileged user, the credentials of the service account used to synchronise Active Directory users over LDAP. In the console the password appears masked.
Proof of Concept
After logging in with administrative credentials you reach the web app
configuration, including the LDAP section. The password is masked in the UI, but by
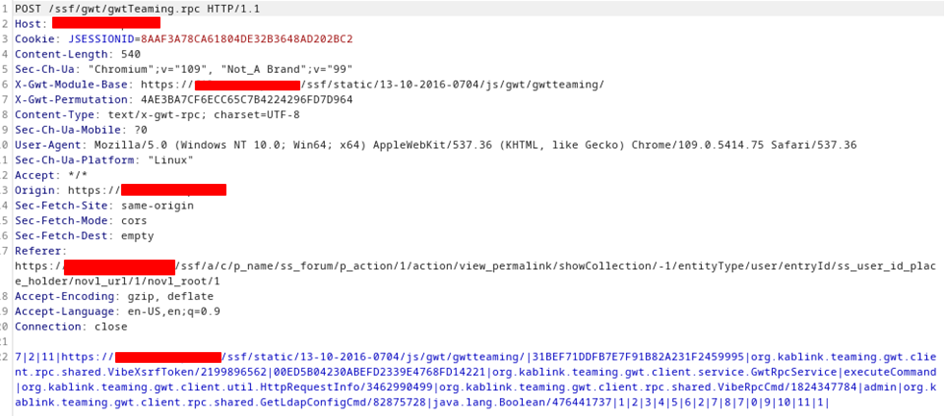
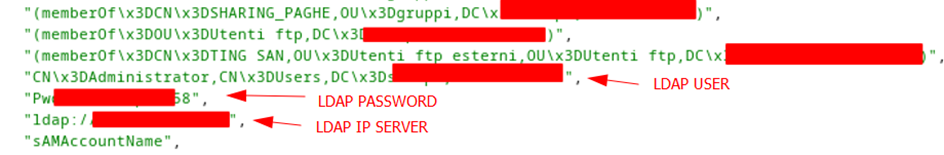
intercepting the POST request to the gwtTeaming.rpc component it appears
in cleartext in the response body.
Impact
The LDAP synchronisation account typically holds elevated domain privileges. An attacker who obtains its password can attempt to access the domain controller with the highest privileges and, from there, exfiltrate sensitive data and deploy ransomware.
Fix and mitigations
The vendor released the patch on 19 May 2023: upgrade the appliance to the latest available version.
Timeline
| Date | Event |
|---|---|
| 2023-01-30 | Vulnerability discovered |
| 2023-03-01 | First contact with the vendor by e-mail |
| 2023-03-07 | Vendor forwards the report to the internal team |
| 2023-04-19 | Vendor confirms handling has started |
| 2023-05-19 | Patch released |
| 2023-06-28 | Security advisory published |
| 2023-12-06 | CVE-2023-32268 assigned |